AI governance frameworks define what an organization is allowed and required to do with AI; operating control is the run-level practice of recording which data a specific result used, so it can be checked against those rules. Policy and run records sit on different layers, and a review usually needs both.
This is the comparison most often miscast as overlap, because both a framework and an operating layer touch words like “governance,” “traceability,” and “trust.” The policy side has never been better codified: ISO/IEC 42001, the first management system standard written for AI, spans lifecycle management, risk and impact assessment, and oversight of suppliers. A framework can name the requirement. It cannot, by itself, satisfy it on the data that a given run actually used. That gap is where most governance programs quietly stall.
What AI governance frameworks do well
Frameworks set the rules. They include internal AI policies, risk taxonomies, and external standards such as the NIST AI Risk Management Framework or the obligations written into the EU AI Act. Forty-seven governments have adhered to the OECD AI Principles, which name transparency, accountability, and robustness, security and safety among their commitments. A good framework tells the organization which use cases are permitted, what documentation each system must carry, and what reproducibility, oversight, and traceability have to exist before a model goes to production.
That alignment is genuinely valuable. It gives legal, risk, and engineering a shared definition of responsible AI, and it turns “be careful with AI” into named obligations that a review board can check against. The NIST framework, for instance, calls for AI systems to be documented, traceable, and auditable. Nobody serious argues the policy layer is optional.
Where the gap opens
The trouble starts at the word “traceable.” Article 12 of the EU AI Act goes as far as text can, obliging high-risk systems to log events automatically across their lifetime so outcomes remain traceable. A framework can restate that duty, yet neither the statute nor the framework holds a mechanism to make any single result reproducible. Between the written policy and an actual audit sits a concrete, unglamorous question: for this specific output, can you show which data state produced it, what changed since the last known-good run, and can you restore that state to inspect it?
If the honest answer is “we’d reconstruct it from scattered logs, notebooks, and a snapshot someone hopefully kept,” the policy is aspirational. The requirement exists on paper; the evidence does not exist at run time. Auditors and regulators increasingly ask for the second thing, not the first, and a binder full of principles does not survive that request.
Operating control: from policy to run records
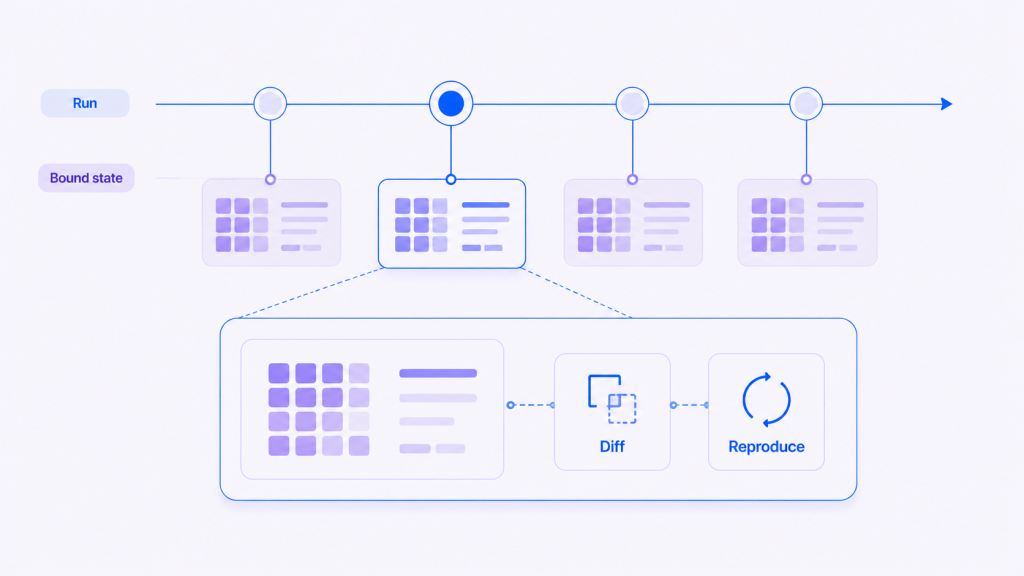
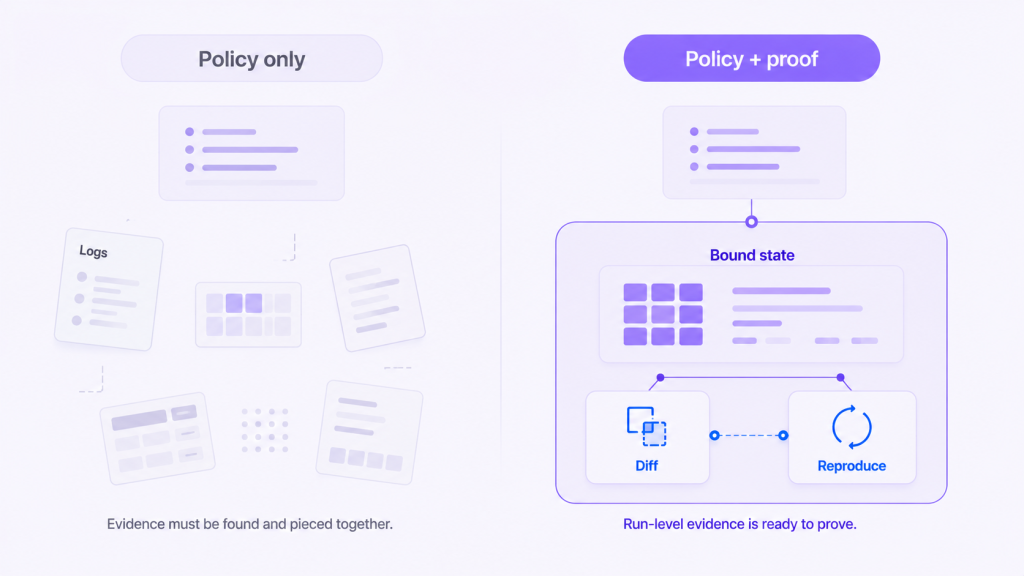
Operating control is the layer that answers the run-level question. It records which data version, settings, and evaluation conditions each AI or agent run used and lets you compare two versions. Where a framework asks for results to be reproducible, operating control gives a team the data record to start from.
Concretely, that means three owned capabilities. A saved data version captures the exact data conditions a run depended on. A run record notes which version, settings, and evaluation conditions the run used, so the link is not a guess later. Comparing with the previous version and re-running on the saved version let a reviewer replay the state, compare it against another, and see precisely what moved. The framework’s Traceability requirement stops being a promise and becomes something you can hand over.
Are AI governance frameworks and operating control competing?
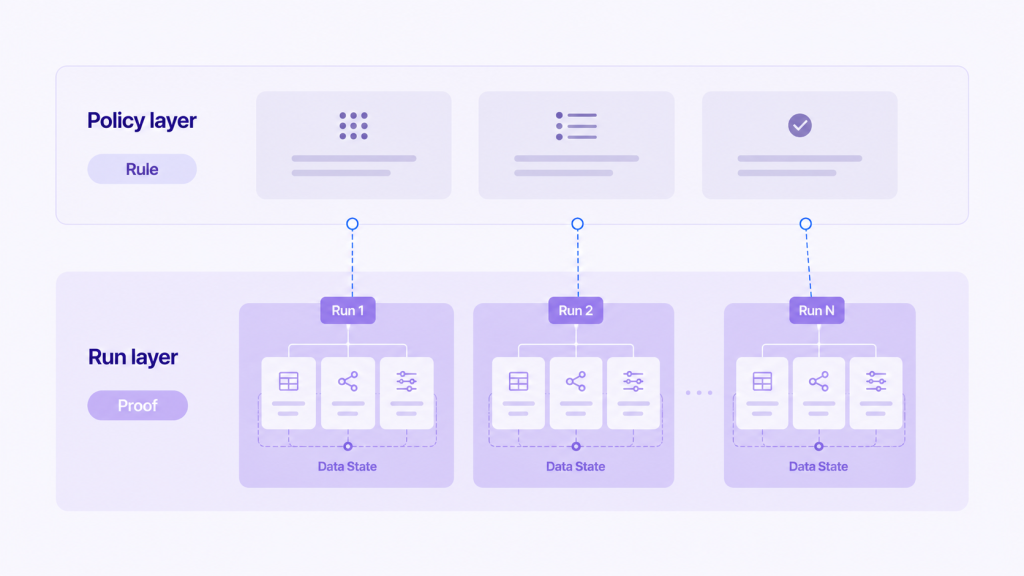
No, and treating them as rivals is the mistake. They are complementary layers of the same program. The framework decides the rule; operating control keeps the run records a team can check against that rule. Policy without run records is hard to check, and run records without policy have nothing to be checked against.
The clearest way to see the split is to line up who owns each responsibility.
Governance defines the rules. Operating control makes a specific AI result reproducible against the exact data state it used.
A quick self-diagnostic
Run your own program through this short test. If you cannot answer several of these with a live artifact rather than a policy sentence, your framework is ahead of your evidence.
- Pick a production AI output from last quarter. Can you name the exact data state that produced it?
- Can you diff that state against the current one and see what changed, without manual archaeology?
- Can you restore the earlier state and re-run to inspect the result?
- When your framework says “traceable,” is there a run-level record that satisfies it, or only the requirement?
- If an auditor asked “show me which data produced this decision,” would you answer with a reproduced state or a promise?
Where it fits in CUBIG’s operating layer
For production AI, the question is not only which model ran; it is which data state and execution conditions produced the result. Syntitan, CUBIG’s AI-Ready Data Platform, reviews enterprise data from six readiness perspectives (Usability, Integrity, Context, Consistency, Reproducibility, and Traceability), prepares what blocks the AI task, and saves each successful result as a new data version while the original data stays unchanged. You can compare each version with the previous one. Linking each AI or agent run to the version, settings, and evaluation conditions it used, and checking a past result again on its saved version, are planned for December 2026.
That is the operating layer beneath your governance framework. The framework names reproducibility and traceability as goals; keeping the data version and conditions behind each run is one practical step toward them. You keep your policy where it belongs, in risk and legal, and add data records that a review can look at. For a deeper treatment of the run-level mechanics, see what Run Binding is, the earlier name for this run record, and how to reproduce an AI incident.
This article compares the concepts; for the same distinction drawn at the product level, with CUBIG’s operating layer set beside AI governance platforms, see CUBIG’s operating layer vs. AI governance platforms.
How to adopt both together
Start from the framework you already have, because it names your obligations. Then, for each requirement that uses the words “reproducible,” “traceable,” or “auditable,” ask what run-level artifact would satisfy an outside reviewer. Then decide how run records can support that artifact. No single tool satisfies a requirement on its own, but a saved data state gives the review something concrete to look at.
Teams that do this in the wrong order tend to buy more policy and more dashboards, then discover at audit time that neither can restore a past state. The order that works is: keep the policy, then add run records. Performance and coverage here are representative until you check them on your own data.
For a worked example of a decision that is later challenged, see how an audit trail for AI decisions in the public sector helps a reviewer look at the data state and execution conditions behind a past decision.
Try it on your data for free. Run a sample proof and see it on your own workflow.